Technology · Security
Secure by design, not by configuration.
Most robot breaches start with an open port or an exposed service. FRP robots have neither.
No way in
Nothing to scan
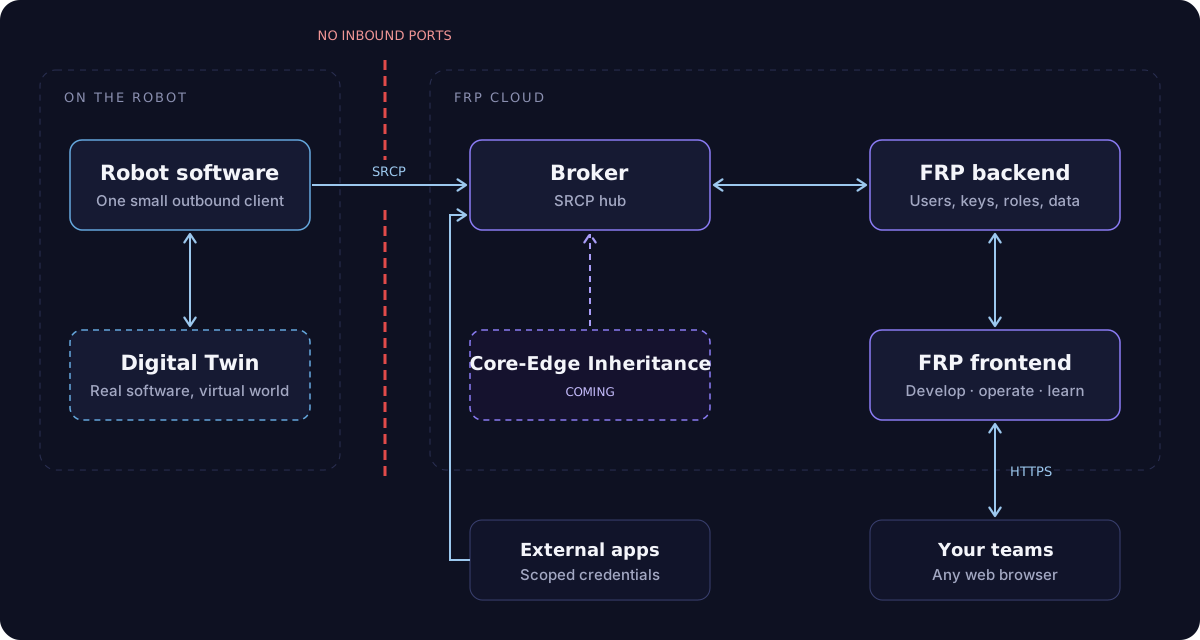
The robot opens no ports and runs no listening services. Its only connection is one it makes itself, outbound, to the broker. That is all it needs, even behind NAT or a mobile network.
Protected payloads
Encryption designed into the protocol
SRCP is built for payload-level encryption with message counters and authentication tags, following IPsec principles, independent of the network underneath.
Central identity
Keys and roles in one place
The FRP backend manages users, keys and role-based access. External applications get scoped credentials for specific robots, never a master key.
Accountability
Every action on record
An audit log records who did what and when, and administrators are notified of important events by email.
Safe operation
Built to fail safe
Liveness checks in both directions, and control sessions released automatically when an operator disconnects.
Process
Audited from the inside
We audit our own code systematically, across robot, broker and platform, and fix findings before release.
Why outbound-only matters
An attacker cannot reach what does not listen.
A robot with an open SSH, video or control port can be found by internet-wide scanners within minutes. FRP robots never accept incoming connections, so there is nothing to find, and no firewall rule to get wrong at a customer site.
See FRP on your robots.
Tell us about your robots, your classroom or your mission. We will show you the platform end to end.